
Rapidly scoring the severity of cybersecurity incidents
2025-07-21 - 8 minutes readChelsea Conard
21 July 2025
In the face of particular natural disasters, stakeholders across sectors are informed of the magnitude. For example, a hurricane may be forecasted with a projected intensity before landfall, while an earthquake is measured and reported with a specific magnitude after it occurs. Cybersecurity incidents pose a similar threat to society; however, there is not an equally clear and standardized mechanism to assess their impact. The challenge to quantify the severity of a cybersecurity incident is crucial for governments, businesses, and organizations to respond to the event effectively. To address this gap, mandated incident reporting requirements are being adopted globally to ensure a consistent framework to understand and mitigate the effects of these incidents.
Incident reporting is critical to collect data on cybersecurity incidents, as it enables impact measurement and informing timely government response. The short shelf life of threat intelligence necessitates early sharing and efficient analysis to support proactive measures. However, reporting requirements vary significantly across countries. For example, China mandates reporting on high-severity incidents within one hour, India requires within six hours of detection, and the United States within 72 hours. These differences are further compounded by the diverse content requirements in each report, highlighting the lack of a standardized approach. This variation in reporting not only hampers global coordination, but also reflects a broader issue that there is often a lack of transparency on how the collected data will be used.
This research creates a scoring mechanism to quantify the severity of a cybersecurity incident, with clear guidelines on how the inputs are calculated to produce a score. We created the Cybersecurity Incident Severity Scale (CISS) to ingest incident data reported within 72 hours and rapidly generate a preliminary score on a scale of 1 to 10, based on the best available information at that time. The score is dynamically updated as an entity submits follow-up reports, ensuring the assessment remains accurate and current. For incidents reported by multiple entities, the data is aggregated to produce a comprehensive view that reflects the collective impact of the incident. Notably, our findings suggest that a small set of well-defined data points is sufficient to generate actionable insights, offering value to all stakeholders.
To develop the scoring system, we drew insights from established scales in other fields like natural disasters and public health, focusing on key indicators that measure the severity and criticality of an incident. Severity is calculated based on anticipated financial loss, harms to individuals, and operational consequences. Individual harm is further broken down by the number of individuals who experience harm to physical safety, the potential exposure of personally identifiable information (PII), the degree of nuisance/distress, financial harm, and operational harm. Criticality is measured as the potential exposure of classified information, captured as the national security impact (NSI), and the incident’s effect on national critical functions (NCFs), as defined in the United States.

The CISS functions by ingesting data collected through a standardized set of questions. The model outputs actionable insights and produces structured data that reflects the current landscape of cybersecurity posture, highlighting areas of vulnerability and identifying strategies to bolster national security. Aggregated data can also be combined with other datasets, such as those from vendors self-attesting through security initiatives, to enrich incident reporting and contribute to vulnerability catalogs. Over time, this growing dataset can support predictive assessments that enable more proactive security measures.
To evaluate the CISS, we applied it to a list of global incidents that encompass all NCFs and incidents that are related to services, data, finances, digital assets, and espionage. Using publicly available sources, we created a dataset designed to replicate the inputs provided in an incident report. While an ideal test would incorporate reports from multiple entities to capture a range of organizational lenses, the limited availability of such data necessitated an approach focused on publicly reported details of the incidents themselves.
We test six methods to compute the final CISS score, and the Spearman and Pearson analyses reveal that the simpler mathematical calculations yield results comparable to more complex ones. We begin by calculating the individual impact score, which is derived by averaging the individual harm scores, covering physical safety, PII, nuisance/distress, financial harm, and operational harm, with their respective population scores. Equipped with the individual impact score, we average the financial and operational scores to determine the severity score. To compute the criticality score, we average the NCF and NSI. Finally, we compute the overall score by assigning 90% to the severity score and 10% to the criticality score. This weighting emphasizes the severity of the incident while allowing the criticality score to serve as a minor multiplier to nudge the score based on the critical nature of the affected function.


The results of the CISS demonstrate the scale’s ability to classify a broad range of cybersecurity incidents. The CrowdStrike Incident, Equifax Data Breach, and SolarWinds received high scores of 7.4, 7.5, and 7.4, respectively.


On the lower end of the scale, the New York MTA Cyberattack in 2021 received a 2.8 and the Russian Radio Station Hijack in 2020 received a rating of 2.7.
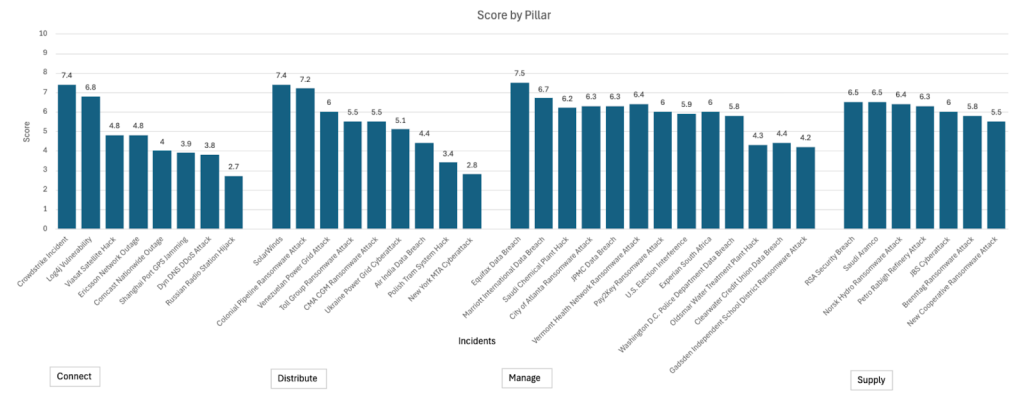
The NCFs framework allows the incidents to be organized according to four overarching pillars: Connect, Distribute, Manage, and Supply. This structure not only facilitates categorization, but also helps identify trends within areas of critical infrastructure. Our research reveals that the Manage pillar accounts for the highest number of incidents, suggesting that functions related to management, such as providing medical care, managing wastewater, and conducting elections, are more frequently targeted or impacted by cybersecurity incidents across the dataset we examined.
The development of the CISS represents a significant step forward to standardize how cybersecurity incidents are measured and assessed. The standardized scale also promotes the harmonization of controls by ensuring that all stakeholders, regardless of their environment, operate under a unified framework. This approach improves coordination during incident response and strengthens the ability to compare and integrate cybersecurity data across sectors and borders, leading to more coherent and effective global cybersecurity strategies. A clear, quantifiable understanding of incident severity also empowers policymakers to allocate resources more effectively, identify systematic vulnerabilities, and implement target interventions.
The report is available here: https://dspace.mit.edu/handle/1721.1/157124
